Cybersecurity Awareness Month for Oklahoma Businesses
Cyber threats can affect organizations of every size, not only large corporations. From customer records and payment details to employee communication and daily operations, businesses depend on...
Read more
Enhanced Simulation Training for Commercial Drivers
Simulation training has become an increasingly important tool for commercial fleets aiming to strengthen driver safety, reduce accidents, and better manage operating costs. By offering controlled,...
Read more
Essential Back‑To‑School Safety Tips for Families
As a new school year approaches, many families focus on fresh routines, supplies, and schedules—making it the perfect time to revisit safety habits. From morning drop‑off to after‑school activities...
Read more
Essential Insights on Cyber Insurance for Businesses
Cyber threats have become a significant concern for organizations of all sizes, making cyber insurance an increasingly important safeguard. With attacks growing more frequent and more sophisticated...
Read more
Back-to-School Traffic Safety Awareness for Families and Drivers
As families prepare for a new school year, roads quickly become busier and demand more caution from everyone. National Traffic Awareness Month in August highlights the importance of staying...
Read more
Risk Management Strategies for Construction Projects
Construction projects involve many moving parts, making them vulnerable to delays, added expenses, and disputes when risks are not properly managed. A strong risk management framework helps teams...
Read more
Back‑To‑School Health Preparation Guide
Preparing for a new school year often revolves around shopping lists, routine changes, and organizing busy schedules. Yet this season also provides a meaningful chance to refocus on your family’s...
Read more
Insurance Planning Tips for College-Bound Families
Sending a student to college brings big changes, and reviewing insurance coverage is one step families often overlook. Even if your student already lives on campus or has been enrolled for a while,...
Read more
Understanding Commercial Umbrella Insurance
Commercial umbrella insurance offers an additional layer of financial protection when a major claim exceeds the limits of your primary business policies. It helps safeguard your company from costly...
Read more
Term Life vs. Whole Life Insurance Explained
Understanding the difference between term life and whole life insurance can feel confusing at first, but breaking down how each policy works makes the decision much clearer. Both types of coverage...
Read more
Reevaluating Life Insurance as Your Income Grows
Life insurance needs change as income and responsibilities expand. While many people purchase coverage with the intention of protecting their loved ones, policies are often left unchanged even as...
Read more
Does Auto Insurance Protect the Car or the Driver?
Auto insurance can be confusing, especially when someone other than the owner is behind the wheel. Many drivers wonder whether the policy belongs to the car or the person driving it. In most...
Read more
A Comprehensive Look at Employment Practices Liability Insurance
Employment Practices Liability Insurance (EPLI) plays a crucial role in helping businesses reduce exposure to claims involving how employees are treated at work. These issues can arise during...
Read more
When Business Growth Moves Faster Than Your Insurance
Business expansion is exciting, but it can also create hidden insurance risks. As your operations advance, the information your policies were originally based on may no longer match your current...
Read more
UV Safety Awareness Month: Everyday Protection That Matters
UV Safety Awareness Month highlights how daily routines can quietly expose your skin to ultraviolet radiation. Even brief moments in the sun—or sitting near bright windows—can contribute to long...
Read more
Overlooked Boat Insurance Risks That Can Leave You Exposed
Many boat owners prepare for the season by tuning up engines, cleaning decks, and planning time on the water, but insurance is often the last thing on their minds. Yet overlooking what your policy...
Read more
Why Job Promotions Are a Smart Time to Reassess Life Insurance
Receiving a raise or stepping into a higher-level role can reshape your financial picture in meaningful ways. These milestones often come with new responsibilities, evolving goals, and increased...
Read more
Smart Add‑Ons: Commercial Insurance Riders You May Want to Explore
Why Insurance Riders Matter for Growing BusinessesAs your business evolves, the risks you face often evolve with it. A standard commercial insurance policy covers many common exposures, but it may...
Read more
8 Common Insurance Myths That Could Leave You Vulnerable
March 11th is Debunking Day, making it the perfect opportunity to clear up some of the most persistent misunderstandings in home and auto insurance. Many people base their decisions on old or...
Read more
Understanding Accelerated Death Benefit Riders: Financial Support When You Need It Most
Accelerated Death Benefit Riders: Financial Support When You Need It MostLife insurance is often thought of as something that helps your loved ones after you’re gone. But what many people don’t...
Read more
Smart Add-On Options to Boost Your Health Insurance Protection
Read more
Spring Construction Insurance: Essential Coverages Contractors Should Review This Season
Why Spring Is a Critical Time for Construction InsuranceAs warmer weather rolls in, construction projects tend to ramp up—bringing more activity, tighter timelines, and increased risk. With...
Read more
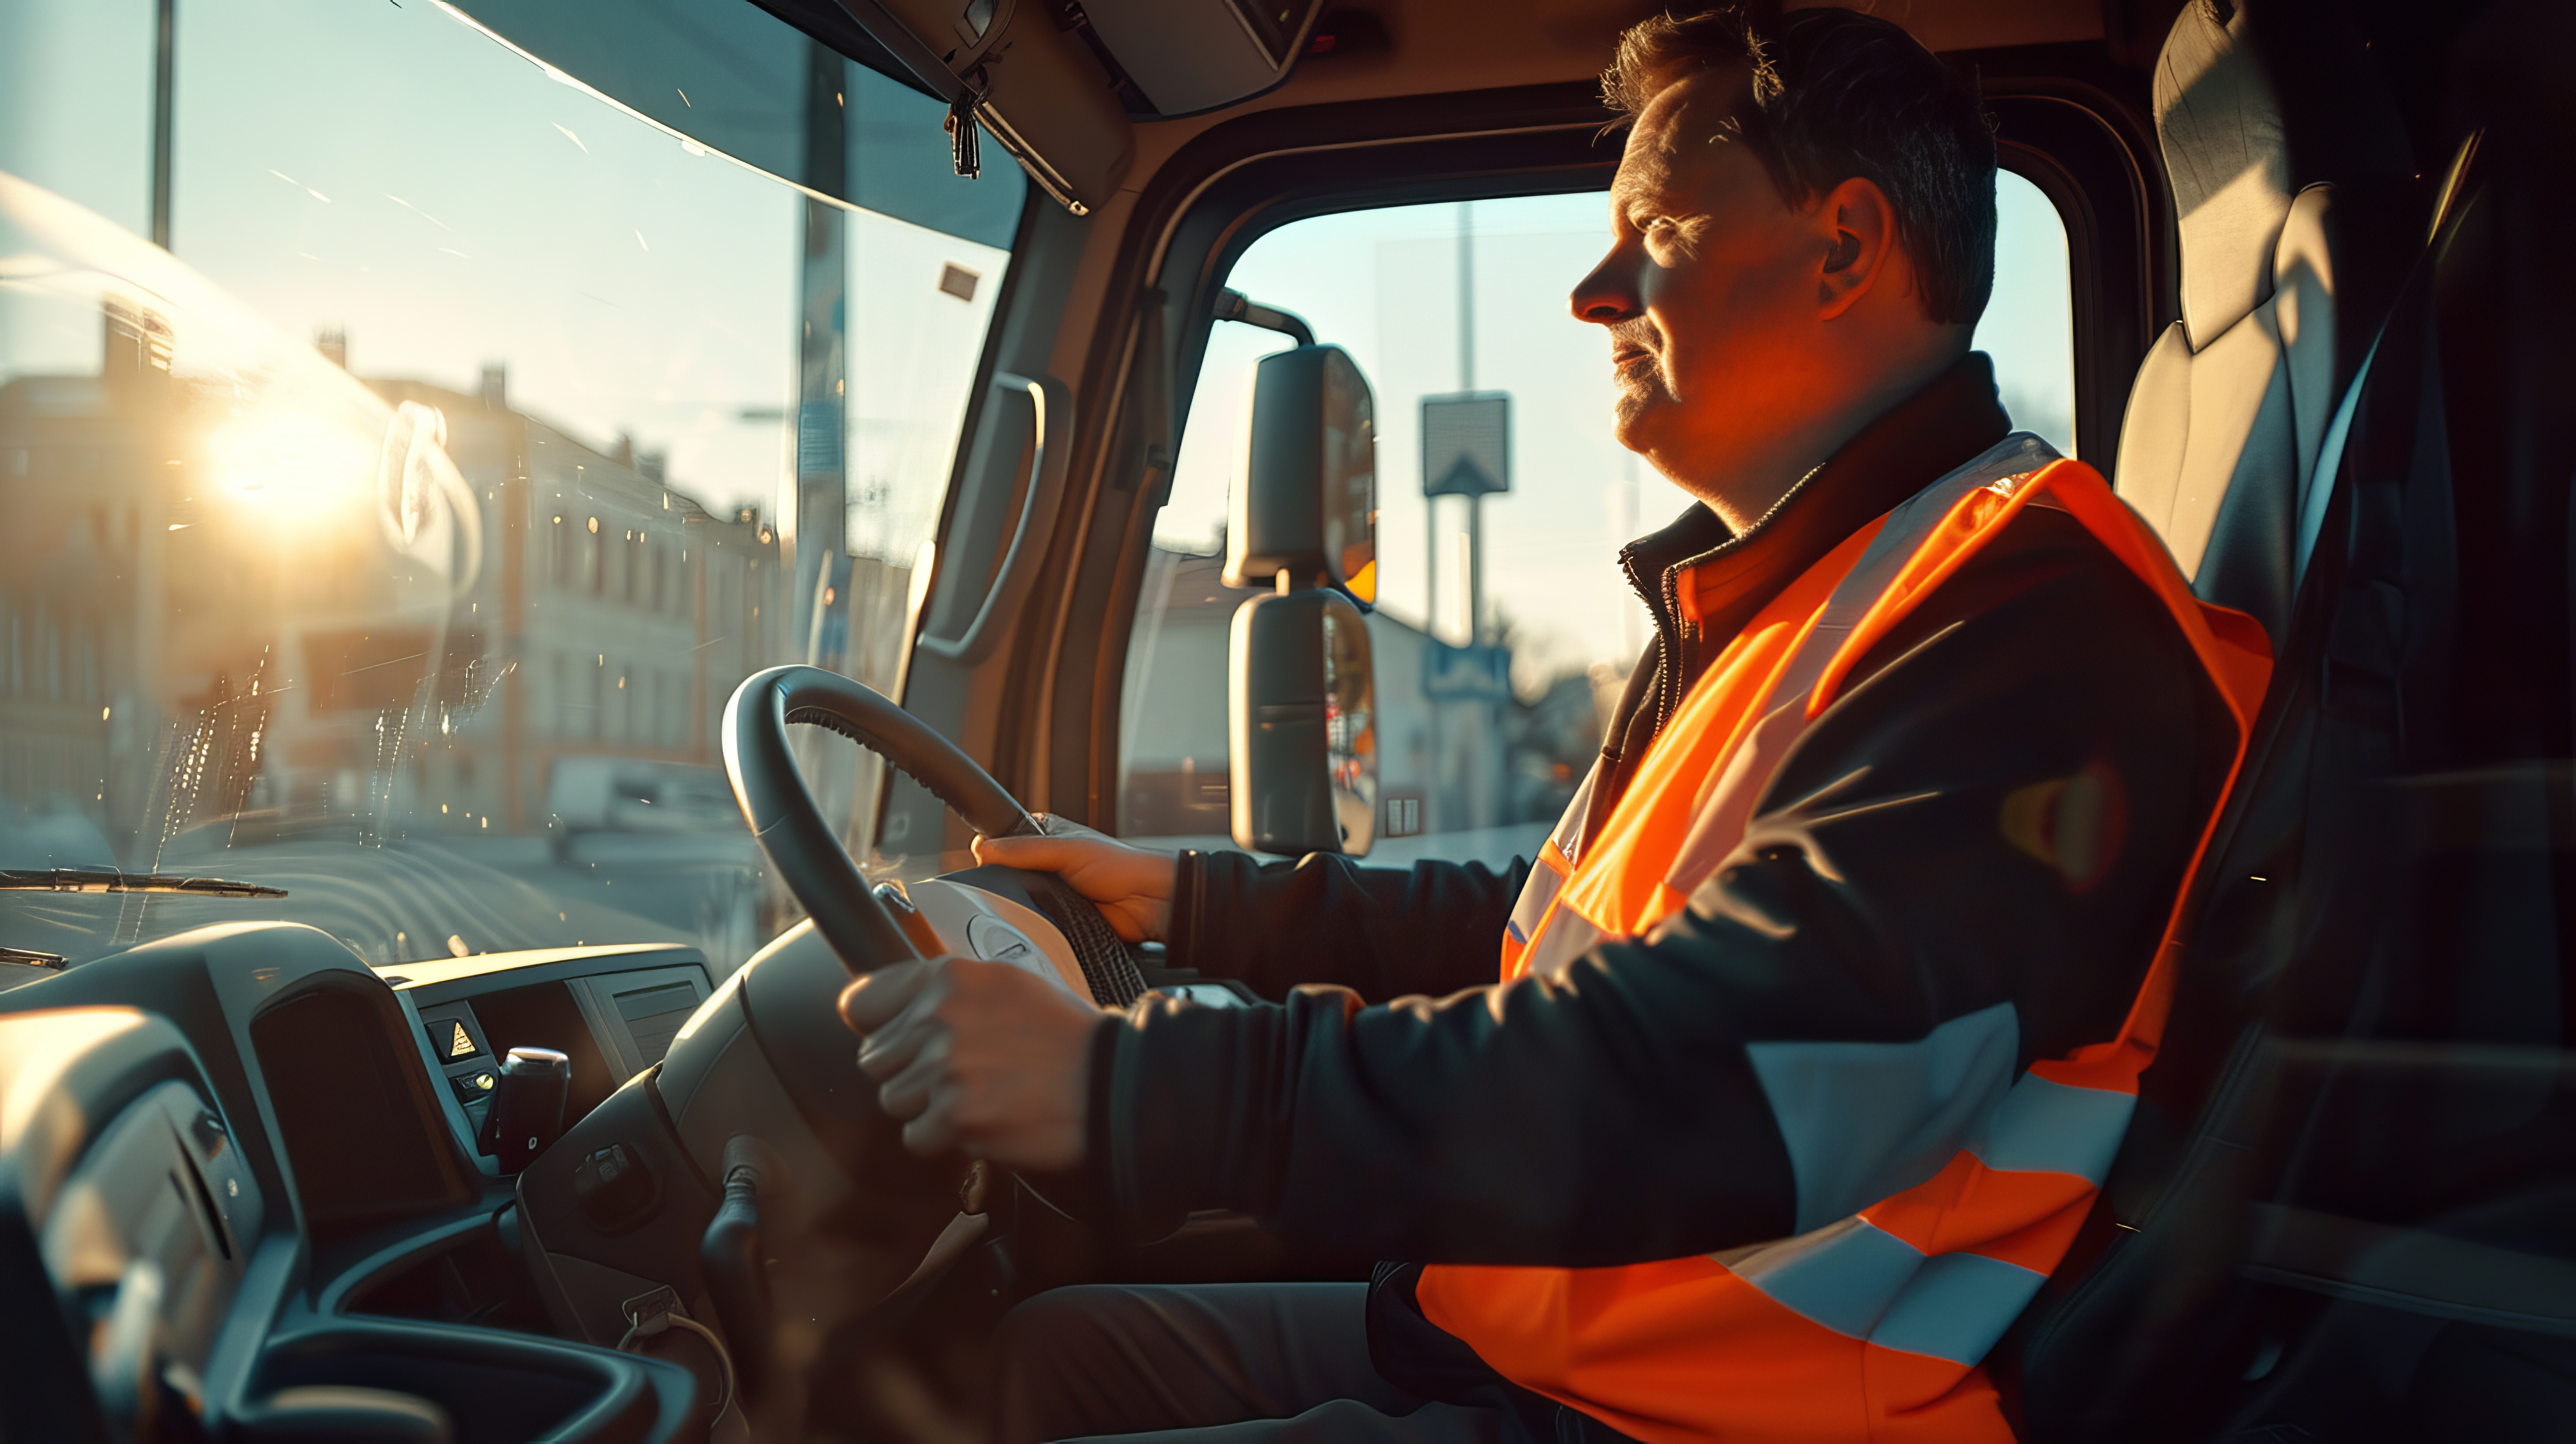
Spring Safety Tips Every Commercial Driver Should Know
As winter fades and spring rolls in, many commercial drivers welcome the warmer weather and longer days. But the new season also introduces fresh challenges on the road. Shifting daylight patterns,...
Read more
6 Key Spring Driving Safety Reminders for a Safer Season
As winter fades and warmer days return, it’s easy to assume driving conditions will automatically get better. But spring brings its own challenges—some of which can be just as risky as icy or snowy...
Read more
Why It’s Worth Taking a Fresh Look at Personal Umbrella Insurance
March is recognized as National Umbrella Month, but the focus here isn’t the kind you carry in the rain. Instead, it’s a reminder to pay attention to a type of insurance that often gets overlooked:...
Read more
Why Commercial Umbrella Insurance Matters More Than Ever
Why Commercial Umbrella Insurance Is Becoming EssentialMarch is National Umbrella Month, making it a perfect opportunity to look at a type of protection many business owners overlook: commercial...
Read more
Essential Insurance Questions Every Small Business Owner Should Understand
Running a small business means juggling countless responsibilities, and insurance often ranks high on the list of confusing but critical decisions. Whether you're just opening your doors or have...
Read more
A Fresh Look at Long-Term Care Riders: An Effective Way to Enhance Your Life Insurance
Preparing for the future isn’t just about building your financial resources — it’s also about preserving what you’ve worked hard to accumulate. Life insurance is a familiar part of that plan, but...
Read more
Contractors vs. Subcontractors: Understanding the Insurance Differences
In construction, every project comes with its own unique challenges—and so do the risks. Whether you operate as a general contractor coordinating major builds or as a subcontractor specializing in...
Read more
Heart Health and Medicare: Key Insights for American Heart Month
February marks American Heart Month, a nationwide reminder to pay closer attention to your cardiovascular well-being. While it’s a great time to break out your red attire, it’s also an opportunity...
Read more
Safeguard Your Valentine’s Day and Presidents’ Day Purchases This February
February may be the shortest month of the year, but it often packs a financial punch. Between Valentine’s Day sparkle, thoughtful gifts, and the rush of Presidents’ Day auto deals, many people make...
Read more
6 Emerging Insurance Risks Businesses Should Prepare for in 2026
As 2026 gets underway, companies are stepping into a business landscape that feels more uncertain than ever. Legal pressures, digital threats, and environmental challenges are evolving quickly,...
Read more
Often-Ignored Home Insurance Riders: Are You Leaving Gaps in Your Coverage?
Many homeowners assume their insurance policy automatically covers every possible scenario, only to discover during a claim that several costly risks require special add-ons. These optional...
Read more
Heart Health Myths Debunked: What You Should Know This American Heart Month
February marks American Heart Month, a national reminder to care for the incredible muscle that keeps your body running every minute of every day. Even though heart disease is still the leading...
Read more

Why Life Insurance Plays a Key Role in Your Financial Well‑Being
January marks Financial Wellness Month, making it an ideal moment to step back and evaluate how all the pieces of your financial life fit together. One area that often gets pushed aside—yet can...
Read more
A Fresh Start Behind the Wheel: Honoring Teen Driving Awareness Month
Celebrating a Major Step Toward IndependenceFor many teenagers, getting a driver’s license represents one of the most exciting transitions into adulthood. It signals new independence, growing trust...
Read more
Safeguarding Oklahoma Businesses and Nonprofits with the Right Insurance
Running a business or nonprofit organization in Oklahoma comes with exciting opportunities – and a fair share of risks. From a Main Street boutique in Oklahoma City to a church or charity in Tulsa,...
Read more
Protecting Your Home, Car, and Family in Oklahoma – A Comprehensive Insurance Guide
Oklahoma is a wonderful place to call home, but living here also means facing unique risks – from spring tornadoes and hailstorms to year-round driving hazards. Having comprehensive insurance...
Read more
Why Choose an Independent Insurance Agency in Oklahoma?
When it comes to protecting your assets and loved ones, the type of insurance agency you choose matters. In Oklahoma, you have a choice between large captive insurers or independent insurance...
Read more

Reviewing your life insurance policies
As we turn the calendar to a new year, a lot of people make major lifestyle changes to ensure they are living their best lives. We never know when our time on Earth will expire. As someone once...
Read more
Do you have the right automobile coverage?
Somewhere around one in four Oklahomans are driving around without car insurance, which is a scary thought. But even more are driving around with inadequate coverage, especially when you consider...
Read more
Making universal life insurance work for you
Universal life insurance is a powerful tool that can be used for many things if it’s set up and managed properly. Large companies have been leveraging the power of universal life insurance for some...
Read more
How medical marijuana could impact insurance
Oklahoma voters recently approved a state question related to medical marijuana. That approval prompted the formation of the Oklahoma Medical Marijuana Authority, and applications are now being...
Read more
View more